Loren Lisk


A Pastebin That Can't Read Your Pastes
FlashPaper
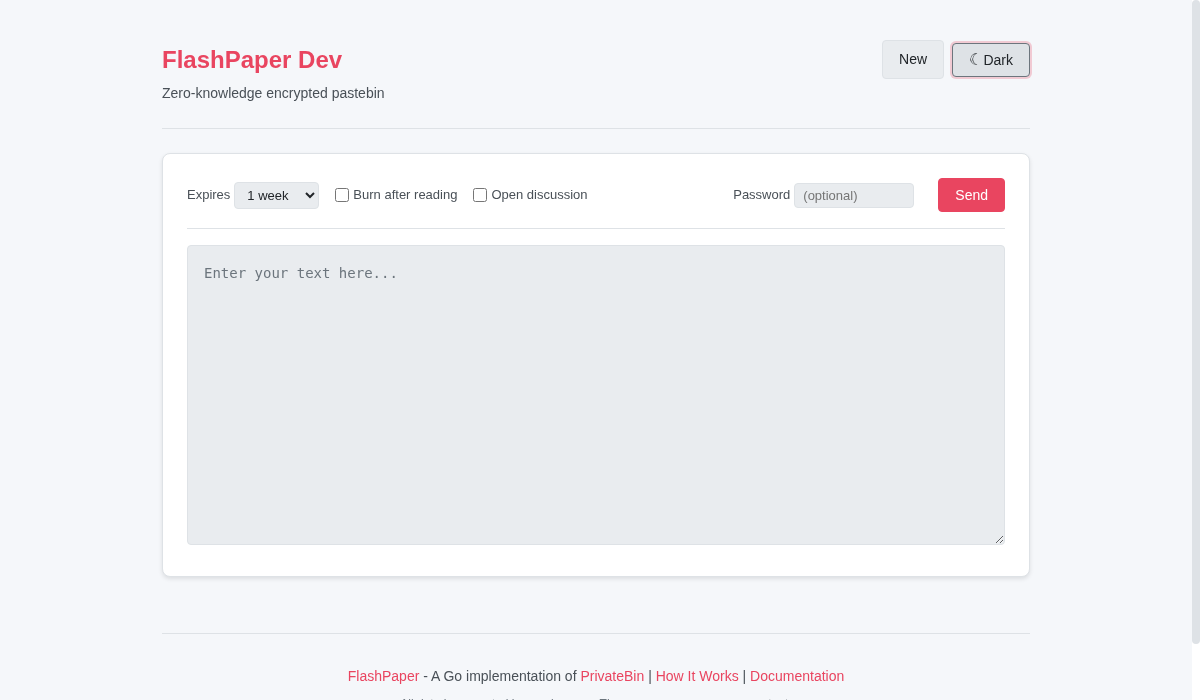
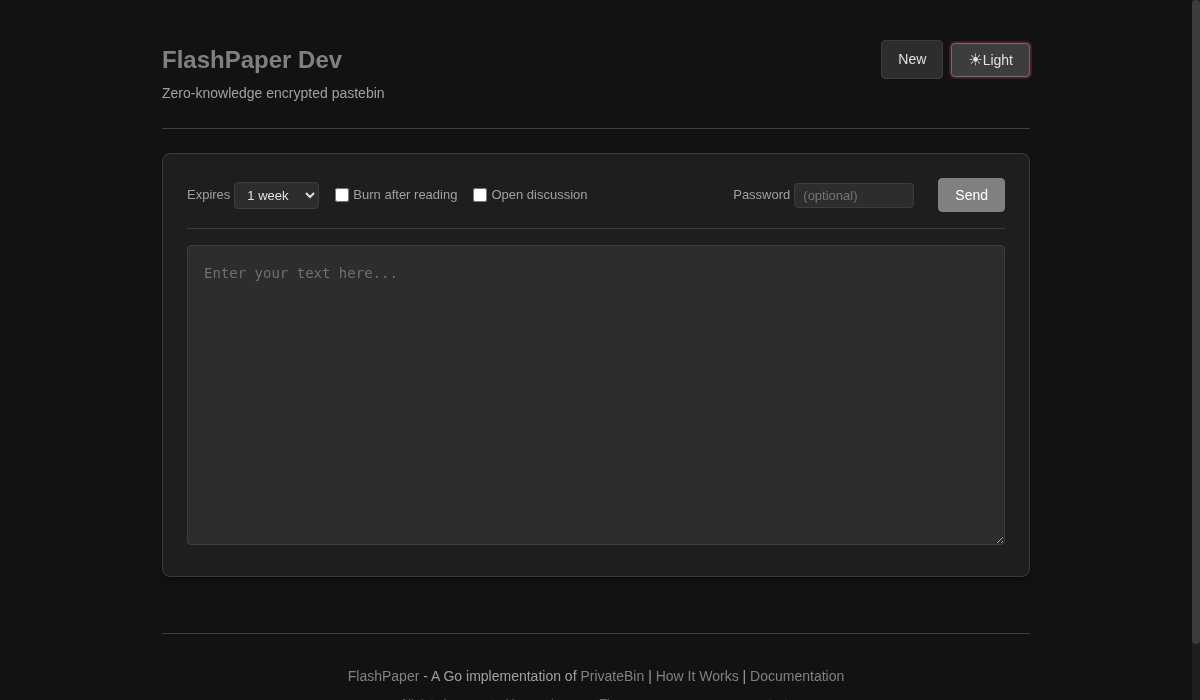
FlashPaper is a zero-knowledge, self-destructing encrypted pastebin written in Go. It reimplements PrivateBin with full API compatibility, so existing PrivateBin clients work against it unchanged.
How zero-knowledge works
The browser generates a random key and encrypts the paste with AES-256-GCM before anything leaves the page. The server only ever receives and stores ciphertext, plus the paste's settings (expiry, burn after reading, discussion). The key travels in the URL fragment, the part after #, which browsers never send to the server.
  Browser                                        Server
  -------                                        ------
  1. generate a random 256-bit key
  2. encrypt the paste (AES-256-GCM)
  3. POST ciphertext + settings  ------------->  store ciphertext
                                 <-------------  paste ID

  share link:  /?<paste ID>#<key>
               \__________/ \___/
               sent to the  stays in the browser,
               server       never sent
The AES key itself is derived from that random key with PBKDF2 (100,000 iterations). A password, if set, is mixed in before that step, so the link alone is not enough to open the paste. And since the server never receives the plaintext, it has no paste content to log.
Features
- Burn after reading - the paste is deleted once it has been viewed
- Expiration - from 5 minutes to never
- Password protection - an extra layer on top of the key in the link
- Discussions - optional threaded comments on a paste
- Storage backends - SQLite, PostgreSQL, MySQL or the filesystem
- Single binary - the frontend assets are embedded in the Go binary
- Dark/light toggle - remembered between visits
Engineering
- Releases - semantic-release cuts versions and the changelog from conventional commits, starting with v1.0.0 in Dec 2025; v1.2.0 in Jan 2026 added OpenTelemetry distributed tracing
- Tests gate the builds - a Go test job runs first, then Playwright end-to-end tests drive the real UI in CI, and the Docker image builds only when both pass
- Kubernetes - Kustomize manifests ship in the repo, with a base and an example overlay
- In production - it runs on the homelab Kubernetes cluster
Links
- Source: github.com/liskl/FlashPaper
- FlashPaper is a Go reimplementation of PrivateBin, which deserves the credit for the design and the API